Automated Cookie Extraction & Tunneling
Extract, decrypt, and tunnel fresh c_user, xs, and datr authentication cookies into persistent sessions without repeated password logins.
What it does
Session management is the backbone of automated Facebook operations. Entering usernames and passwords repeatedly triggers security alerts and password reset loops. FBVerse Bot v3.7 features a dedicated Cookie Extraction & Tunneling module.
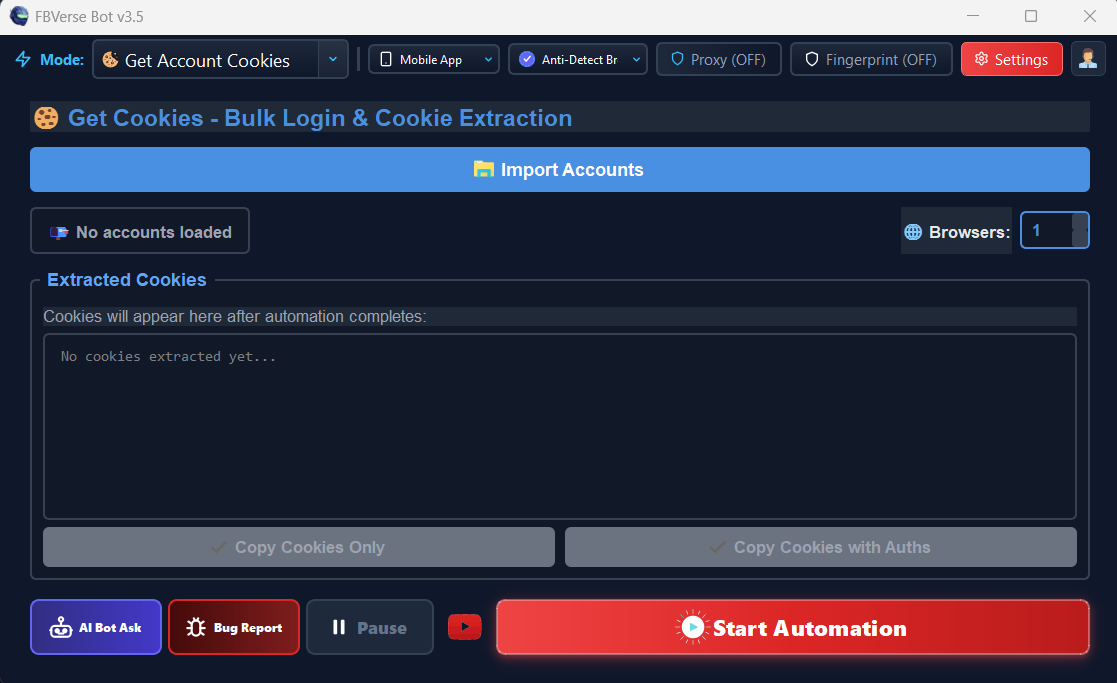
Effortlessly extract fresh c_user, xs, fr, and datr cookies from newly logged sessions. Convert cookies into standardized JSON or Netscape format, test cookie validity in milliseconds, and tunnel sessions straight into anti-detect profiles without ever typing a password.
How it works
Open the Get Cookies tab
Select active browser windows or load accounts.
Batch extract
Capture c_user, xs, datr and the rest from many sessions at once.
Validate and inject
Check every cookie's live status, then inject straight into anti-detect profiles.
Key capabilities
- Supported Cookies: c_user, xs, datr, fr, sb, wd, presence, locale
- Formats Supported: JSON Arrays, Base64 Token, Netscape HTTP Cookie File
- Health Checker: Sub-Second Live Check for Valid / Expired / Checkpoint State
- One-Click Injector: Instant Session Cookie Management into Anti-Detect Browser Profiles
- Batch Extraction: Extract Cookies from 50+ Logged Browser Sessions Simultaneously
- Encryption: Local AES-256 Encrypted Session Token Storage
Results depend on account age, setup quality, proxies, and how the tool is used day to day.
Tips for best results
Validate right before use - a cookie that was live yesterday may not be today.
Export a JSON backup of every extraction batch.
Never type passwords on flagged networks; cookies skip the login checkpoint entirely.
Keep extracted cookies on your own machine - the storage is AES-256 encrypted locally.
Common questions
Which cookies does it capture?
The full Facebook session set: c_user, xs, datr, fr, sb and supporting cookies - everything a profile needs to resume a session.
What formats can I export?
JSON arrays, Base64, or Netscape cookie files - compatible with most tools that accept cookie imports.
Why use cookies instead of passwords?
Every fresh password login is a checkpoint risk. Injecting an existing session cookie resumes the account the way a returning browser would, and team members can work without ever seeing the password.
Related features
Try Automated Cookie Extraction & Tunneling today
The free 24-hour trial includes every feature. No card required.